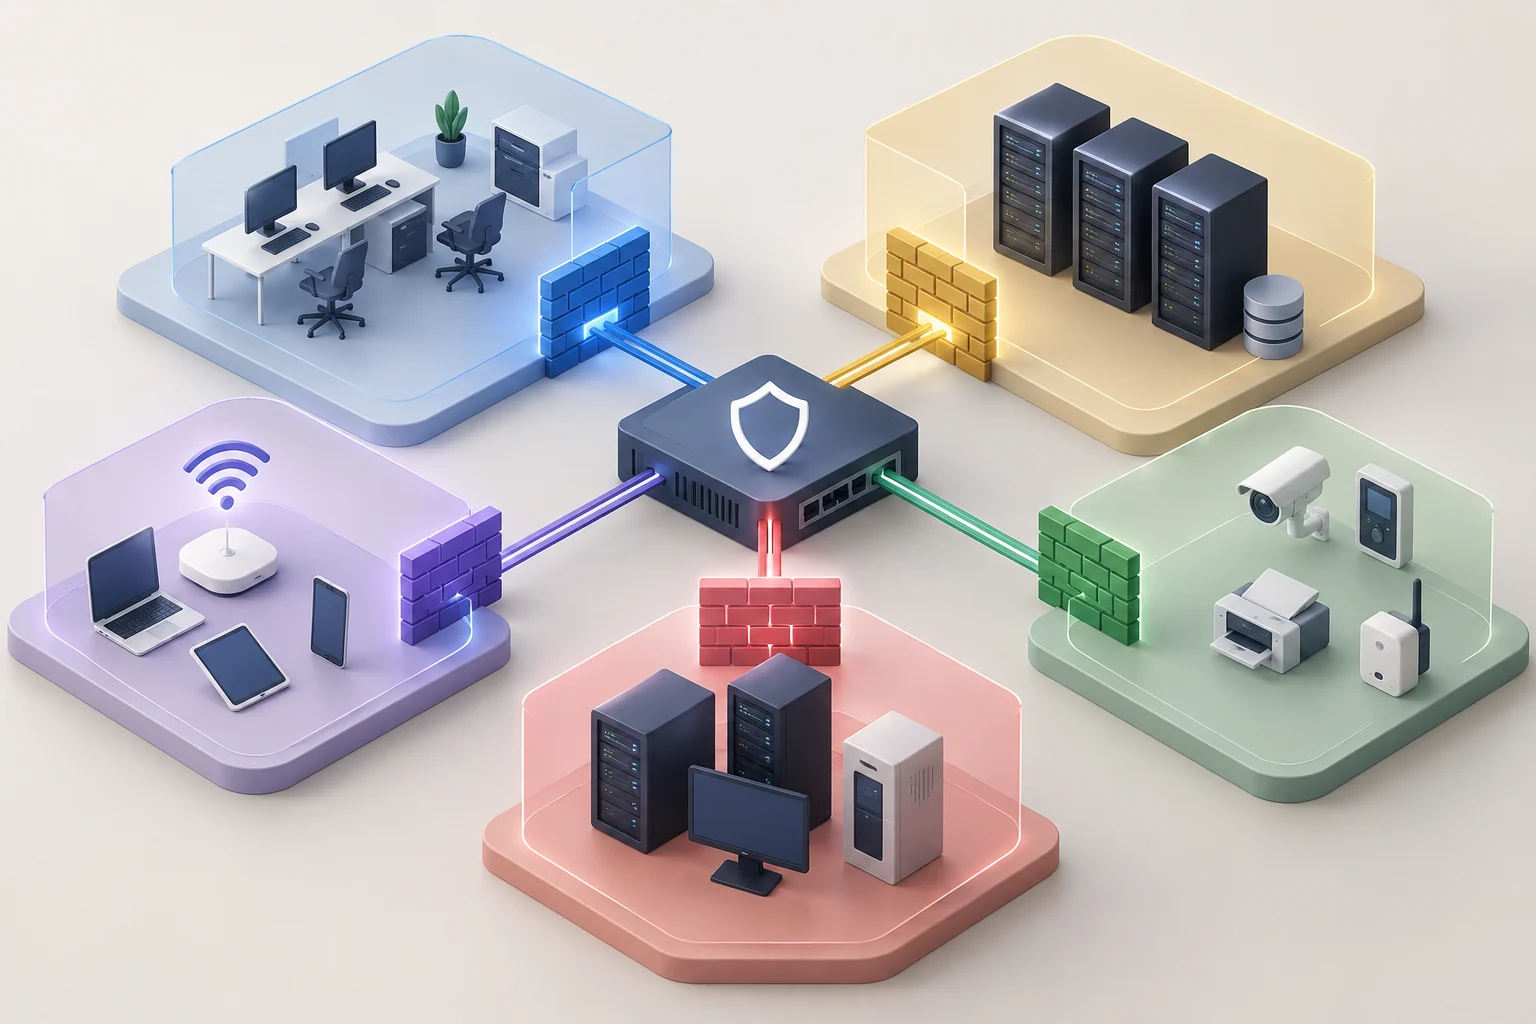
Network segmentation is a security practice that divides a computer network into separate sections, or segments, to control how devices and systems communicate. Access rules can be applied between these sections, limiting which users, devices, or services are allowed to exchange data. This reduces unnecessary network exposure and can help contain security incidents if one segment becomes compromised.
For example, a hospital can separate medical equipment, employee devices, guest Wi-Fi, and administrative systems into different network segments. A compromised guest device would therefore have limited access to critical systems. Network segmentation is useful for improving security, controlling access, reducing the spread of threats, simplifying network management, and protecting sensitive resources.